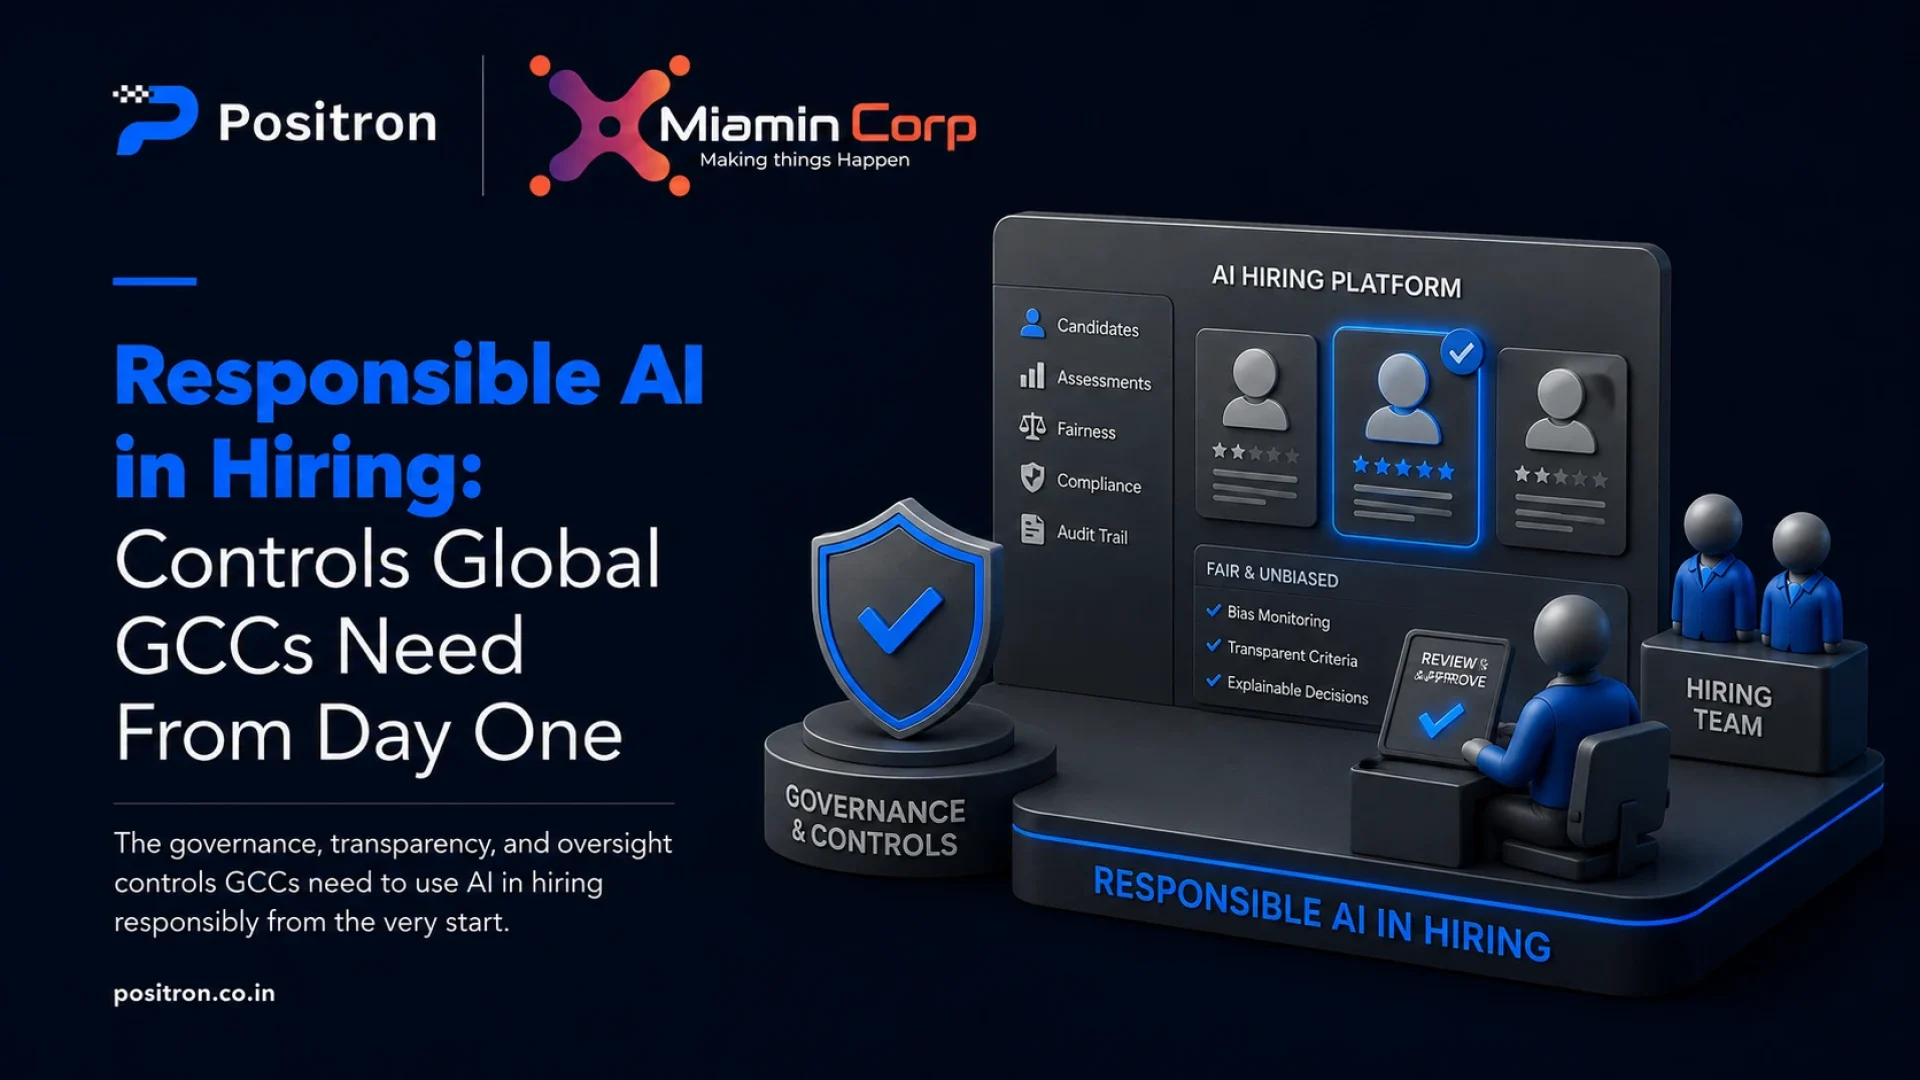
Global GCCs need a use-case register, jurisdiction review, accountable ownership, vendor evidence, data controls, job-relevance testing, meaningful human oversight, candidate transparency, monitoring and a stop-use process. Local employment and data rules still require specific review.
In our latest article, we set out the controls needed from day one and explain why governance must continue after launch and after every material vendor change.
The responsible use of AI in hiring begins before a tool evaluates its first candidate.
It begins when the enterprise decides what the tool is allowed to do, which data it may use, who is accountable for its output and how a person can challenge a harmful decision. If those controls are added after deployment, the GCC may already have inconsistent records, unsuitable vendor terms and decisions it cannot explain.
This is a global operating issue because one hiring workflow may serve several jurisdictions. The laws are not identical, and risk can depend on where the candidate is located, where the employer operates, what the system does and how its output affects a decision.
Build a use-case register
Inventory every hiring tool or feature that uses automated scoring, ranking, inference or generation. Include functions embedded in applicant-tracking systems and vendor platforms, not only products marketed as AI.
For each use case, record its purpose, users, candidate population, data inputs, model or service provider, output, decision influence, jurisdictions, retention, integrations and accountable owner. Distinguish administrative automation from a system that influences access to employment.
An inventory turns “we use AI in recruitment” into governable questions. It also exposes shadow features switched on during a software update or used by an external recruiter without central approval.
Classify risk by use and jurisdiction
The EU AI Act identifies certain AI systems used for recruitment, selection and worker management as high risk. At the time of this review, the European Commission’s current implementation page says rules for stand-alone systems in listed high-risk areas, including employment, apply from 2 December 2027. The implementation timetable changed in 2026 and must be rechecked before publication or deployment. Legal advice is required for a specific system.
Other jurisdictions use different approaches. New York City’s Local Law 144, for example, imposes bias-audit and notice requirements for covered automated employment decision tools. UK data-protection expectations and US anti-discrimination law add different duties and risk tests. A global standard can set a strong minimum, but it does not remove local assessment.
Put nine controls around the lifecycle
Accountable ownership
Name a business owner, not only a technology administrator. Define approval, escalation and stop-use authority across talent, legal, privacy, security, accessibility and AI governance.
Vendor due diligence
Require documentation on intended use, training and evaluation data where available, limitations, subprocessors, security, change notifications, audit support and incident handling. A vendor assurance statement is evidence to examine, not responsibility transferred.
Data governance
Use data that is necessary, lawful and relevant to the job purpose. Document provenance, quality, retention and access. Do not infer protected or sensitive characteristics merely because a model can.
Job relevance
Connect every assessment feature to the actual work and required capability. Convenience or correlation is not enough. Keep evidence for why the method is appropriate.
Pre-deployment testing
Test accuracy, reliability, accessibility and differential outcomes on relevant populations and workflows. A vendor’s global test may not represent a GCC’s roles, languages or candidate market.
Human oversight
Define which outputs require review, what evidence the reviewer sees and when the reviewer must override or escalate. The reviewer needs time, competence and authority; a ceremonial approval click is not meaningful oversight.
Candidate transparency and accommodation
Explain the material use of automated tools in clear language where required or appropriate. Provide a route to request reasonable accommodation, correct data and raise a concern.
Ongoing monitoring
Track selection outcomes, errors, overrides, complaints, drift and vendor changes. Review by role, stage and relevant group where lawful and statistically meaningful.
Incident and retirement controls
Define when use is paused, who is notified, how affected decisions are reviewed, and how data, access and integrations are removed when the tool is retired.
Use frameworks without confusing them with law
NIST’s AI Risk Management Framework organises voluntary practices around Govern, Map, Measure and Manage. ISO/IEC 42001 specifies an AI management system for organisations that develop or use AI. Both can help create repeatable governance, but neither automatically proves compliance with employment or data-protection law.
The UK Information Commissioner’s 2024 recruitment-tool audits reported concerns including excessive data collection, indefinite retention, unfair filtering and inference of gender or ethnicity from names. Those findings came from a specific set of consensual audits, but they show why procurement questions must be tested against real product behaviour.
Responsible AI is not a one-time bias audit or policy statement. It is a controlled lifecycle with visible ownership, evidence and the ability to stop. The right time to build it is before the first hiring deadline makes governance feel inconvenient.
Frequently Asked Questions
What are the biggest GCC trends in India?
Are GCCs in India still mainly technology centers?
Why is AI important for India GCCs?
What should companies watch before setting up a GCC in India?
Sources
- European Commission — AI Act Overview and Implementation Timeline — current at 12 August 2026.
- EUR-Lex — Regulation (EU) 2024/1689, including Annex III — 13 June 2024.
- NIST — Artificial Intelligence Risk Management Framework 1.0 — 26 January 2023.
- ISO — ISO/IEC 42001:2023, AI Management System — December 2023.
- UK ICO — AI Tools Used in Recruitment — 6 November 2024.